Trust & validation
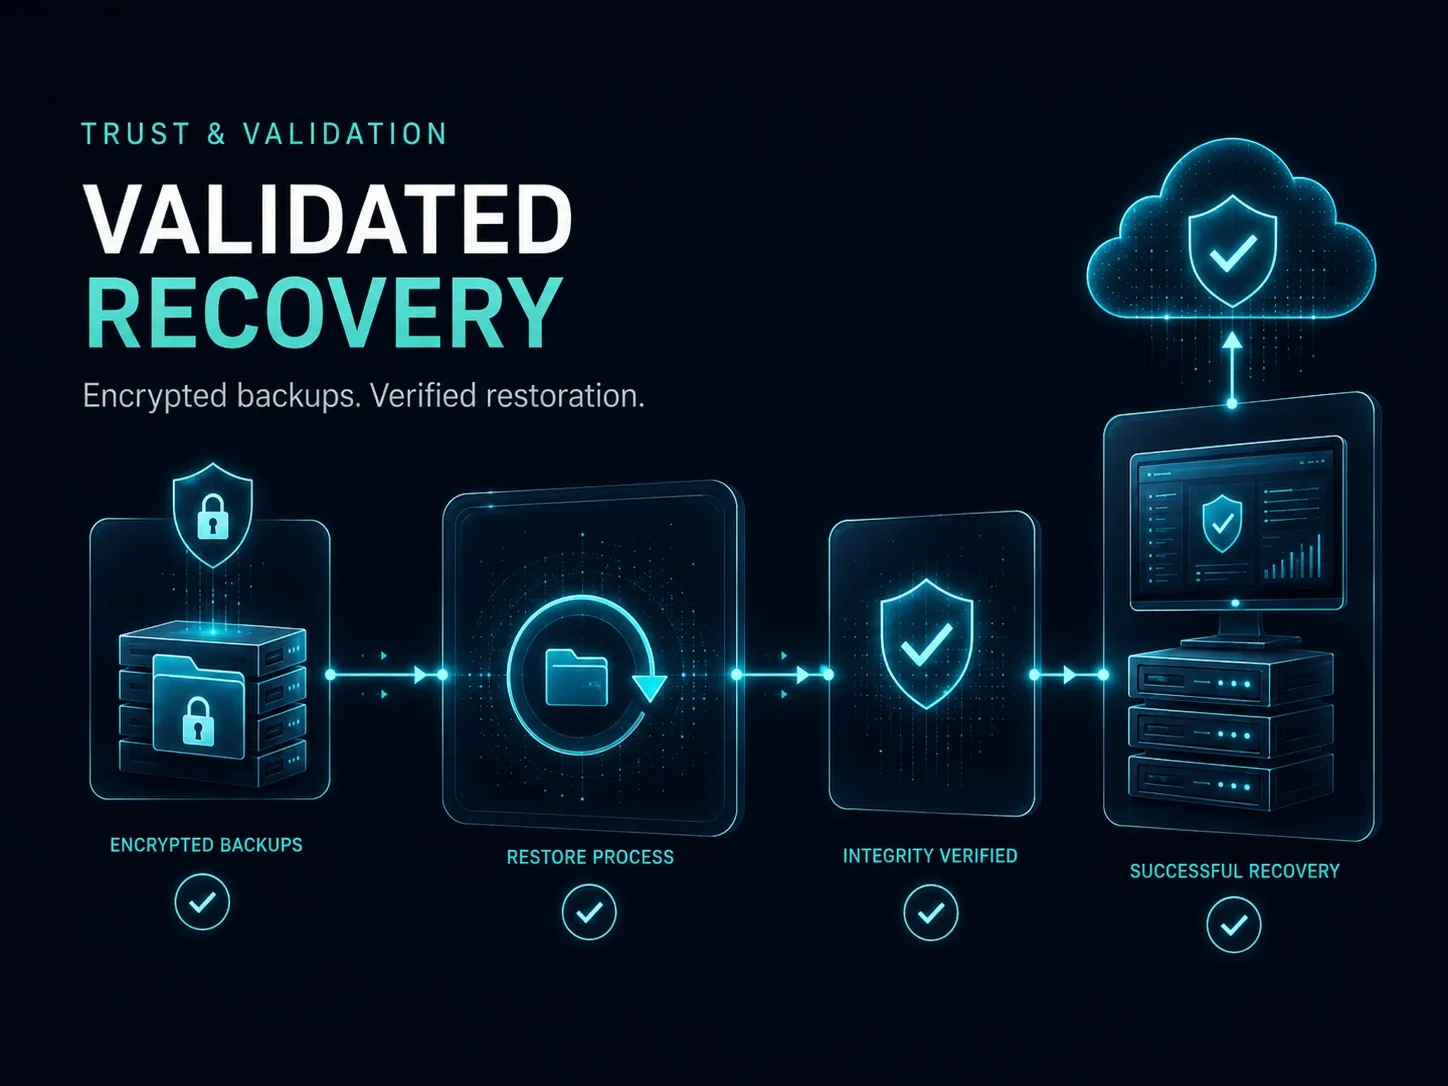
Trust should be demonstrated, not assumed.
VESTA combines independent trust domains, contextual authorization, encrypted objects, minimal metadata and recoverable generations. The architecture is then tested against explicit failure and compromise scenarios.
Architecture principles
High assurance without publishing an attacker’s implementation manual.
Selected public patent foundation
Patented research co-invented by HES co-founder Bertrand F. Cambou.
These public patents support the credibility of the cryptographic research foundation without revealing VESTA’s implementation details.
Patent notice. VESTA is developed with High Entropy Security and references public inventions co-authored by HES co-founder Bertrand F. Cambou. Public patent records list Northern Arizona University and, for certain patents, the United States Department of the Air Force as assignees. These references do not imply that VESTA owns the patents.
Technical due diligence