How VESTA is different
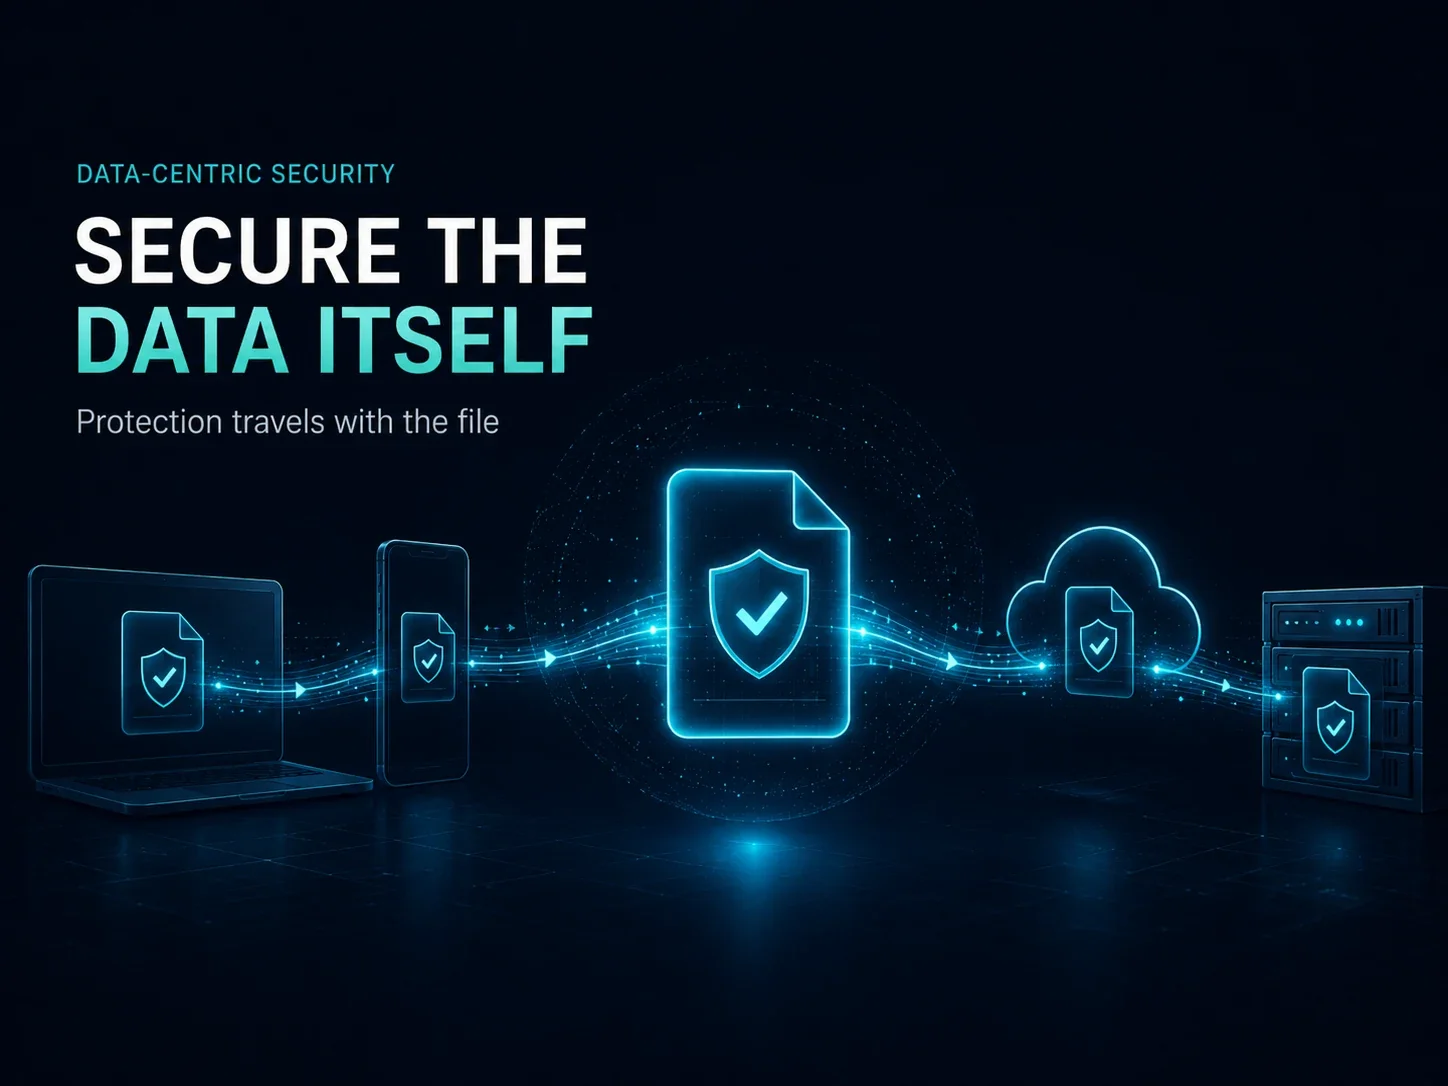
Encryption usually ends when access begins. VESTA protects the decision to decrypt.
Most solutions like E2EE protect data at rest or in transit, then rely on the same identity, application or key service to release readable content. VESTA adds a separate cryptographic release boundary. Reaching the file is not enough.
Conventional control versus VESTA
Four decisive differences. One consequence: access is not decryption.
Explore how the security outcome changes across access, trust, compromise and recovery. The description remains intentionally high level to protect confidential and patentable mechanisms.
Encrypted virtual drive
New protection without changing every business application.
Users and applications access protected files through a familiar virtual-drive interface. Outside an authorized operation, the underlying data remains encrypted.
This separates protection from the business application. VESTA policies, audit and recovery can remain independent even when the application, endpoint or storage environment is compromised.
Compatibility is announced and remains subject to validation for each supported deployment profile.
A compromised login may reach the file without becoming sufficient to reveal it.
VESTA addresses the last security boundary: the controlled moment when encrypted content is allowed to become readable.
Planned MCP and AI-assisted recovery
Find a deleted or previous version without giving AI the power to decrypt it.
A planned VESTA MCP Server will help authorized users search recovery history in natural language, for example by filename, path, date, user or version.
The AI interface will not hold decryption authority. Search, preview and restore requests remain subject to VESTA permissions, independent security controls and audit.
AI helps locate the right recovery object.
VESTA remains responsible for authorization, protected release, audit and recovery integrity.
Assess the final boundary
Who can make your most sensitive data readable today?
A focused review maps the point where a compromised authority could currently become sufficient.